Agent governance and audit, run by agents
AI agents act on data with no consistent approval, record or rollback. Here is how Data Workers runs it instead.
Key takeaways
- •The problem today. AI agents act on data with no consistent approval, record or rollback.
- •What changes. Every agent change goes through the gate: diff, blast radius, named approver and a hash-chained receipt.
- •What stays with your people. Autonomy levels and policies: risk owners set them.
- •The result. Every AI action is approved where it matters and auditable everywhere.
The problem today
AI agents act on data with no consistent approval, record or rollback.
What changes with Data Workers
Every agent change goes through the gate: diff, blast radius, named approver and a hash-chained receipt.
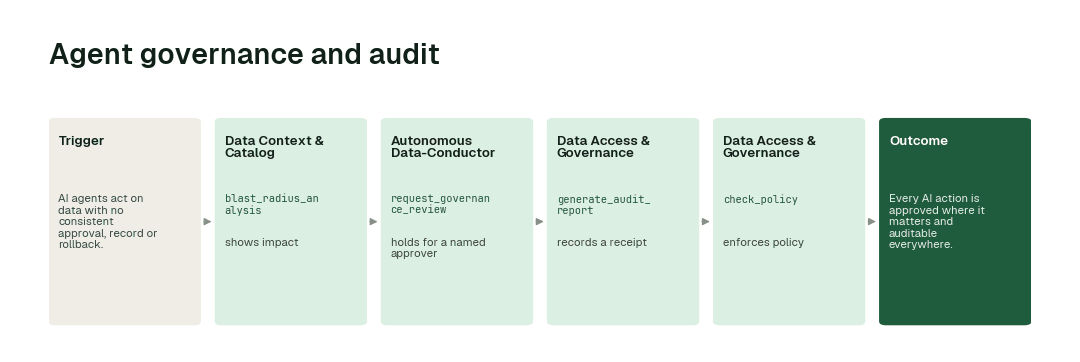
The workflow, step by step
- 1.The Data Context & Catalog agent calls
blast_radius_analysisand shows impact. - 2.The Autonomous Data-Conductor calls
request_governance_reviewand holds for a named approver. - 3.The Data Access & Governance agent calls
generate_audit_reportand records a receipt. - 4.The Data Access & Governance agent calls
check_policyand enforces policy.
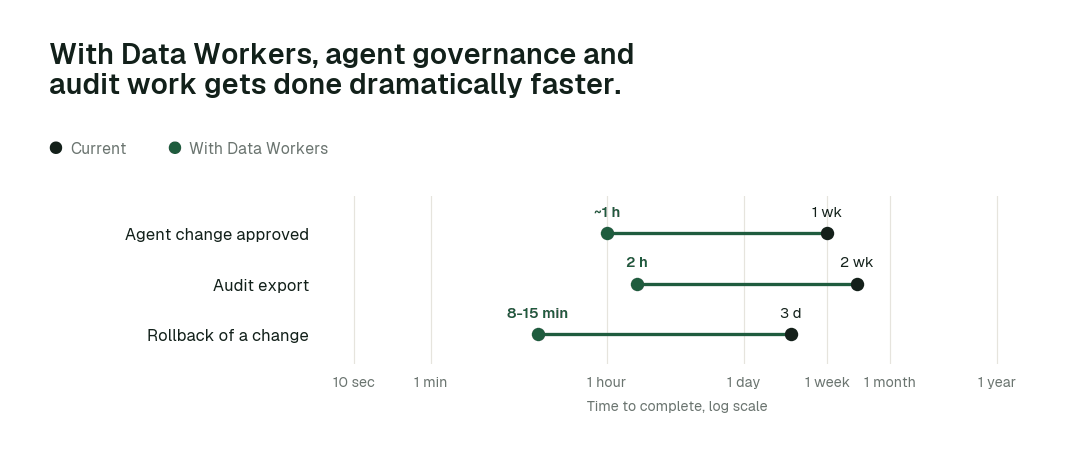
The impact metrics we move
- •Agent change approved: from about a week to ~1 h
- •Audit export: from about 2 weeks to 2 h
- •Rollback of a change: from about 3 days to 8-15 min
What goes on autopilot
- •Every action is receipted, so audits are fast.
- •Autonomy is set per domain, so risk stays bounded.
Where your people stay in charge
Autonomy levels and policies always go to a named approver, because risk owners set them. Everything starts at L1, observing only, and autonomy rises only on evidence.
The pilot
- •Scope. The gate on one domain.
- •First week. Agents run at L1, observing only, and show the fixes they would have made, with receipts.
- •By week two. The routine work above runs on its own; anything sensitive stays with a named approver.
- •At day 30. We review the impact metrics against your baseline:
- •Agent change approved: from about a week to ~1 h
- •Audit export: from about 2 weeks to 2 h
- •Rollback of a change: from about 3 days to 8-15 min
- •Cost. Start with a pilot ($7,500 one-time, credited in full against the first year). Scale is from $1,000 a month and Enterprise from $3,000 a month, billed annually, with unlimited seats, no usage meter and no markup on model spend. See pricing.
Related: The AI and automation page · The full team playbook