You're on Ataccama: ONE Governs Quality, Master Data and the Catalog. Data Workers Repairs the Cause Upstream and Proves It
Ataccama governs DQ rules, master data and the catalog. Data Workers diagnoses each Data Trust Index drop across the estate, fixes it behind approvals and verifies it.
Your governance office runs on Ataccama ONE. Glossary terms carry the DQ rules that define good data, critical data elements are flagged, and DQ monitors evaluate the rules on schedule, pushed down into Snowflake or Databricks. The Data Trust Index tells risk, finance and your AI programme whether a dataset is cleared for use. ONE MDM keeps the golden record, ONE RDM the code lists, and freshness SLAs and pipeline monitoring raise alerts that notify Teams or Slack and escalate to a Jira or ServiceNow ticket. Since August 2026 the rebuilt ONE AI Agent can run a full governance pass on a catalog item, asking before it changes anything. Ataccama ONE governs the data in one place: quality, the master record and the catalog. Data Workers repairs what breaks it in every system upstream, and proves the repair to the steward.
Ataccama is the smoke alarm, wired into the governance office. Data Workers is the crew: when a rule on a CDE fails, the cause usually sits outside Ataccama, in an Informatica mapping, an Airflow DAG or a core banking release, and Data Workers finds it, fixes it behind approvals and leaves a receipt.
Key takeaways
- •Ataccama keeps its job. Rules, the Data Trust Index, MDM, the catalog and the ONE AI Agent stay with your governance office.
- •A failed rule arrives with a diagnosis. The failed rule reaches Data Workers through the on-call, whose assistant can use Ataccama's MCP server side by side with Data Workers; Data Workers traces the cause across Oracle, Informatica PowerCenter, Airflow and Snowflake, and maps everything downstream.
- •One change set, one named approver. The mapping change, the reload and a new check go to the owner in Slack or email; nothing runs until they approve in Spellbook.
- •Verified, then handed to the steward. Data Workers queues the rerun and checks every table the fix touched; the steward resolves the ticket with the receipt link.
- •Autonomy per domain. KYC, finance and risk each climb from L0 manual to L4 autonomous at the pace your governance office sets.
Ataccama is the steward's system. Data Workers is the crew.
Here is a Tuesday at a European retail bank across Oracle core banking, Informatica PowerCenter, Airflow, Snowflake, Ataccama ONE, Jira Service Management and Microsoft Teams. Times are CET. This is an illustration, not a customer case.
| Time | System | What happens |
|---|---|---|
| Sat 22:00 | Oracle core banking | A quarterly release widens TAX_ID and starts writing foreign tax identification numbers with a two-letter country prefix |
| Mon 23:30 | Airflow and PowerCenter | The kyc_nightly DAG starts the wf_kyc_customer_extract workflow, which loads KYC.CUSTOMER in Snowflake. The target port still holds 11 characters, so 12,400 foreign TINs are cut short. The session reports success |
| Tue 01:10 | Snowflake | The DAG's next task rebuilds KYC.CRS_REPORTABLE_ACCOUNTS, the table behind the bank's Common Reporting Standard file |
| 02:00 | Ataccama ONE | The KYC monitor runs its TIN validity rule with Snowflake pushdown; 12,400 records fail and the Data Trust Index on the CDE customer.tax_id falls below threshold. ONE MDM holds 380 records as suspect matches, since the tax ID is a match key |
| 02:01 | Ataccama and Teams | The alert posts to the KYC stewardship channel in Teams |
| 02:10 | Data Workers | Reads the alert, its findings and the DQ results over Ataccama's API and MCP server. Lineage runs from the Snowflake table back through the DAG run to the PowerCenter session. Every failing value is exactly 11 characters while Oracle holds 13 or 14: truncation at the extract. Blast radius: the CRS table, the CRS file job due Thursday, the AML screening view and the MDM queue. It opens a Jira Service Management ticket for the KYC stewardship group with the diagnosis and posts a finding card to Teams |
| 02:25 | Data Workers | Proposes one change set: widen the PowerCenter target port and the Snowflake column to 20 characters (with rollback SQL), rerun Monday's load, and add a length-parity check between the extract and KYC.CUSTOMER |
| 08:15 | Spellbook | The ETL owner reviews the diagnosis and blast radius and approves; the ETL team applies the change through the bank's change process at 09:30 |
| 09:40 | Airflow | Data Workers queues the kyc_nightly rerun for Monday's run date |
| 10:30 | Snowflake and Ataccama | Data Workers verifies load lag against its baseline, row counts against the session's source count, TIN validity and the new check. The steward reruns the monitor and the Data Trust Index recovers, the MDM steward releases the 380 records, and the KYC steward resolves the Ataccama alert and the Jira ticket with the receipt link |
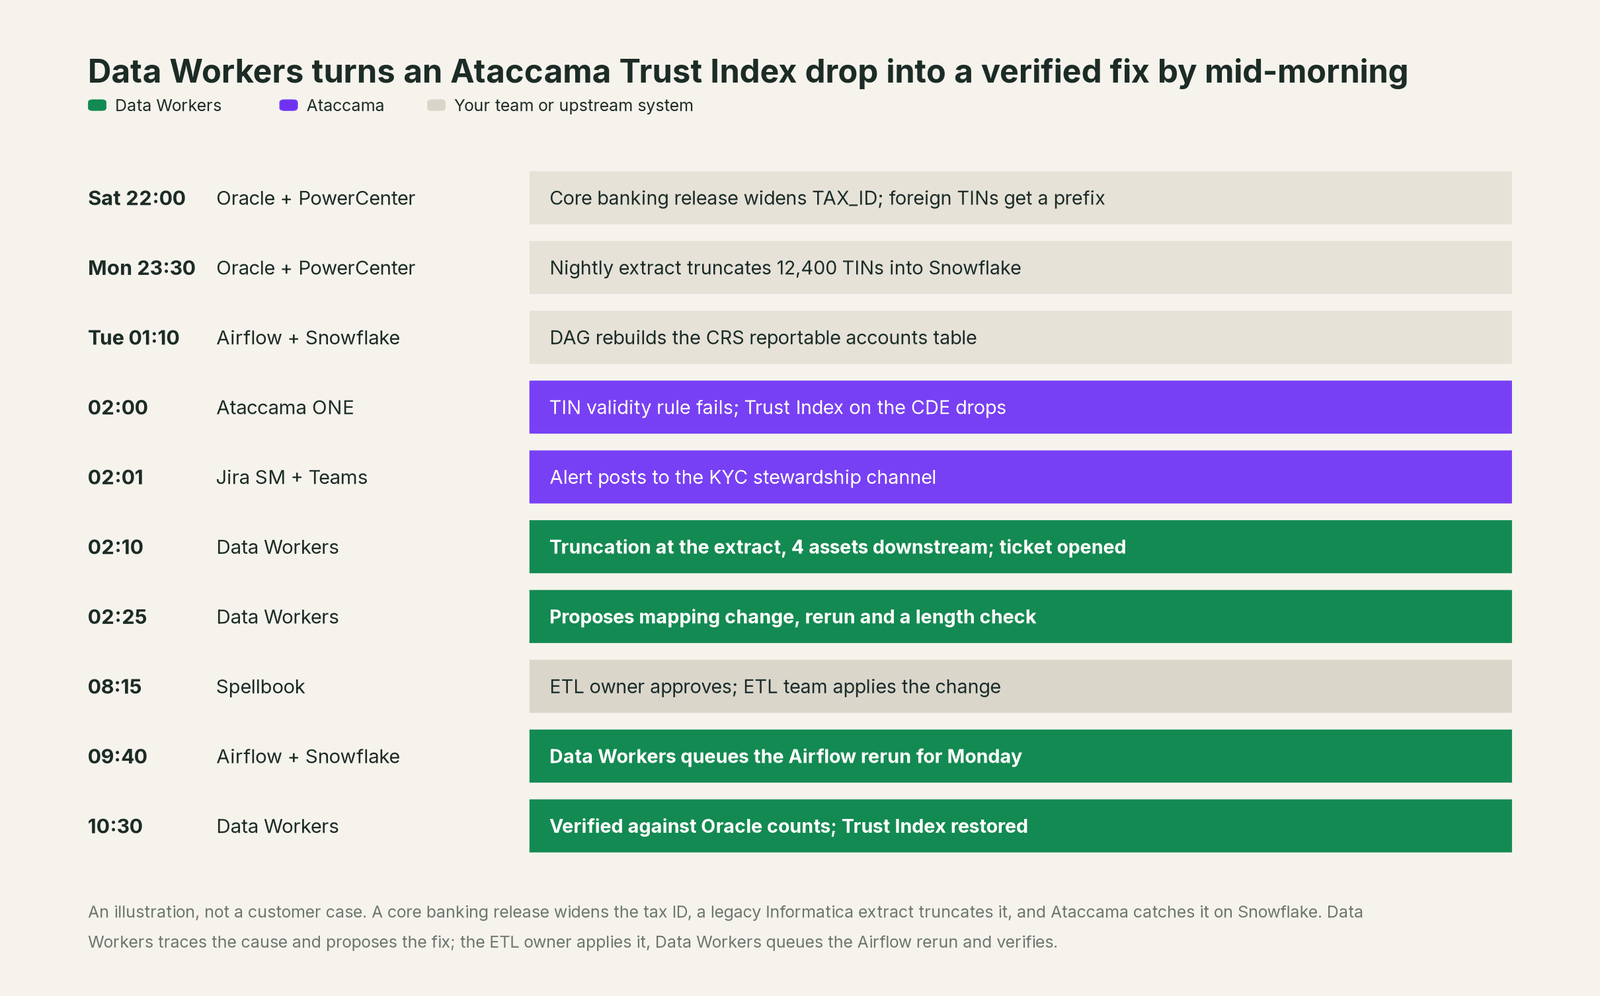
Ataccama did what a governance platform should: the rule fired on the right records, the Data Trust Index warned everyone off the table, and MDM refused to merge on bad keys. What changed is everything after the alert. The steward woke up to a diagnosis that reached a truncated port in a ten-year-old PowerCenter mapping, a blast radius that included Thursday's regulatory file, and one change set for the ETL owner.
| Job | What Ataccama does | What Data Workers does |
|---|---|---|
| Defining good data | DQ rules on glossary terms and CDEs, cross-table rules, DQ gates in pipelines | Reads those rules as context and runs its own checks on the tables it repairs |
| Detection | DQ monitors, anomaly detection, freshness SLAs and pipeline monitoring raise findings and alerts | Watches freshness, volume and schema itself, so many breaks are caught before a rule fires |
| Scoring and routing | The Data Trust Index scores readiness; alerts notify Teams or Slack and escalate to Jira or ServiceNow | Joins the alert to lineage, pipeline runs, schema changes and incident history to find the cause |
| The fix inside Ataccama | The ONE AI Agent creates rules, flags CDEs, edits reference data and assigns stewards, with approval before each change | Leaves rules, terms and stewardship to Ataccama |
| The fix outside Ataccama | Invalid records go to the steward | Proposes the change to the mapping, pipeline or table with blast radius, routes it to a named owner and queues reruns after approval |
| Verification | The next monitor run updates the score | Checks freshness, volume, schema and quality on every downstream table the fix touched |
| The record | Alert, findings, DQ history and the escalated ticket | A receipt: the cause, the change, who approved it, what it touched, how it was verified and how to undo it |
Why doesn't Ataccama just do this itself?
Because Ataccama has drawn its line carefully, and it is the right line for a governance platform. The ONE AI Agent works on Ataccama's own objects, asks you to approve each action that modifies data or metadata, and lets you revert any change in Review changes. Ataccama's governance page says its AI features produce "suggestions that require human review and acceptance before taking effect." The MCP Trust Layer is read-only by design, and so is the alerts API added in September 2026: to resolve or escalate an alert, you use the web application.
Stewards and auditors trust the Data Trust Index because the platform that produces it is not also changing the data it scores. Changing an Informatica mapping, rerunning an Airflow DAG and reloading a Snowflake table is a different product with a different liability: each change must be checked downstream, approved by its owner, reversible, verified and recorded. Data Workers is built for that job, and leaves the scoring to Ataccama.
Every tool owns a slice. Data Workers covers the whole lifecycle
Ataccama owns data quality: rules tied to business meaning, CDEs, mastering and a trust score the whole bank reads. Each point tool adds another console, another contract and another handoff. Data Workers covers the whole lifecycle with one context, one approval flow and one audit trail.
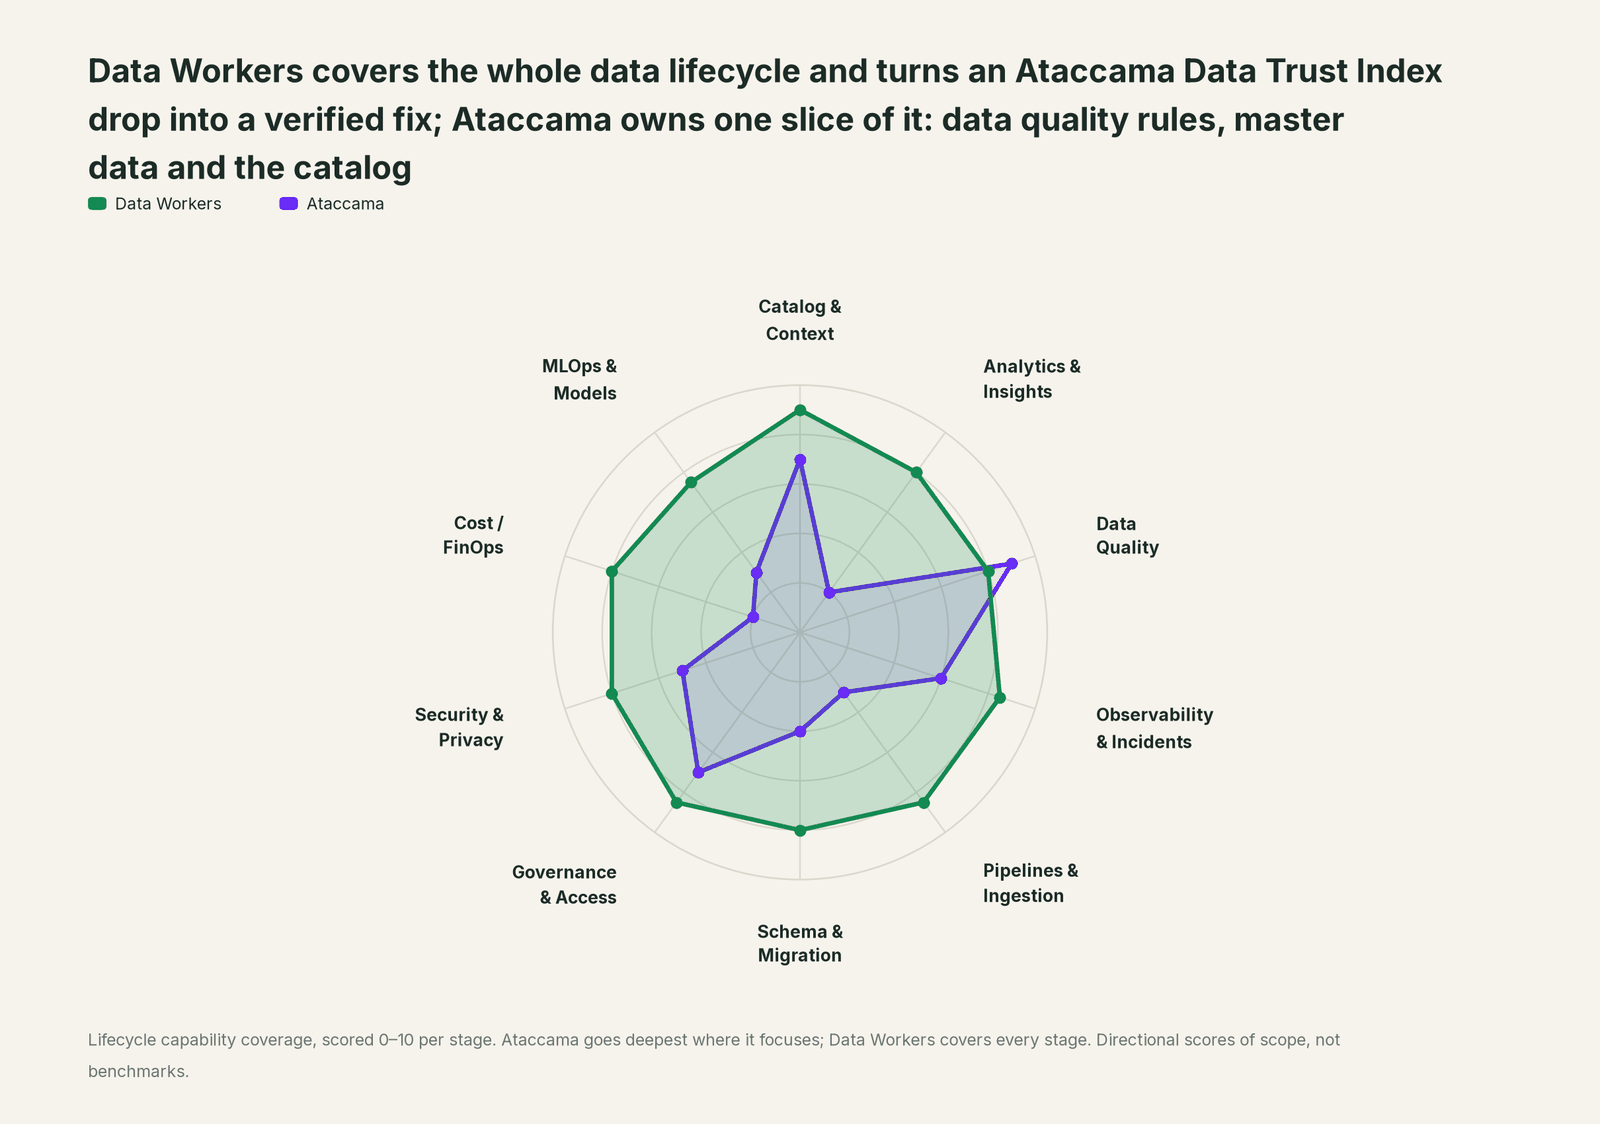
| Stage | Data Workers | Ataccama | Why we scored it this way |
|---|---|---|---|
| Catalog & Context | 9 | 7 | Ataccama ONE's catalog, glossary, lineage and critical data elements give the governance office a governed inventory. Data Workers keeps one governed context graph of definitions, owners, lineage, quality and usage across every platform. |
| Analytics & Insights | 8 | 2 | Data Stories builds charts on catalog data, and the ONE AI Agent answers questions about assets. Data Workers answers data questions from governed definitions with lineage behind every number. |
| Data Quality | 8 | 9 | Ataccama's home stage: DQ rules tied to glossary terms and CDEs, DQ monitors, DQ gates in pipelines, cross-table rules and the Data Trust Index. Data Workers runs checks too and fixes the cause when a rule fails. |
| Observability & Incidents | 8.5 | 6 | Freshness SLAs, anomaly detection and OpenLineage pipeline monitoring raise alerts and escalate them to Jira or ServiceNow. Data Workers diagnoses across systems, fixes with approval and verifies the fix. |
| Pipelines & Ingestion | 8.5 | 3 | DQ gates, and the Data Quality API (Early Access Preview since August 2026), can stop a pipeline when quality breaks. Data Workers queues reruns and backfills through your orchestrator, with approvals. |
| Schema & Migration | 8 | 4 | Data observability flags schema changes on monitored tables. Data Workers scores a schema change's blast radius, drafts the migration with rollback SQL and plans moves in waves. |
| Governance & Access | 8.5 | 7 | Stewardship groups, governance roles, MDM golden records and reference data are core strengths. Data Workers dry-runs each warehouse access request and proposes a time-bound grant for the owner to approve. |
| Security & Privacy | 8 | 5 | Data protection classifications and metadata-first AI controls. Data Workers' pull request review flags new columns whose names or annotations look sensitive, and leaves a receipt on every data change. |
| Cost / FinOps | 8 | 2 | Ataccama does not manage warehouse spend. Data Workers reads warehouse spend next to each incident and drafts setting changes for their owner. |
| MLOps & Models | 7.5 | 3 | Ataccama certifies the data behind AI with trust signals. Data Workers keeps the data under your models fresh and correct. |
For the category view, read Data Workers vs data observability and beyond data observability: autonomous resolution. For SLAs a governance office can hold a team to, see data quality SLA examples.
How Ataccama and Data Workers work together
Spellbook Data Catalog (in preview) is where data owners review each proposed change, see who approved it and roll it back. Data Context Wizard keeps one governed context graph, the Data-Agents Swarm does the work with 20+ specialist agents, and the Autonomous Data-Conductor runs each fix end to end: detect, diagnose, fix, review, verify, remember.
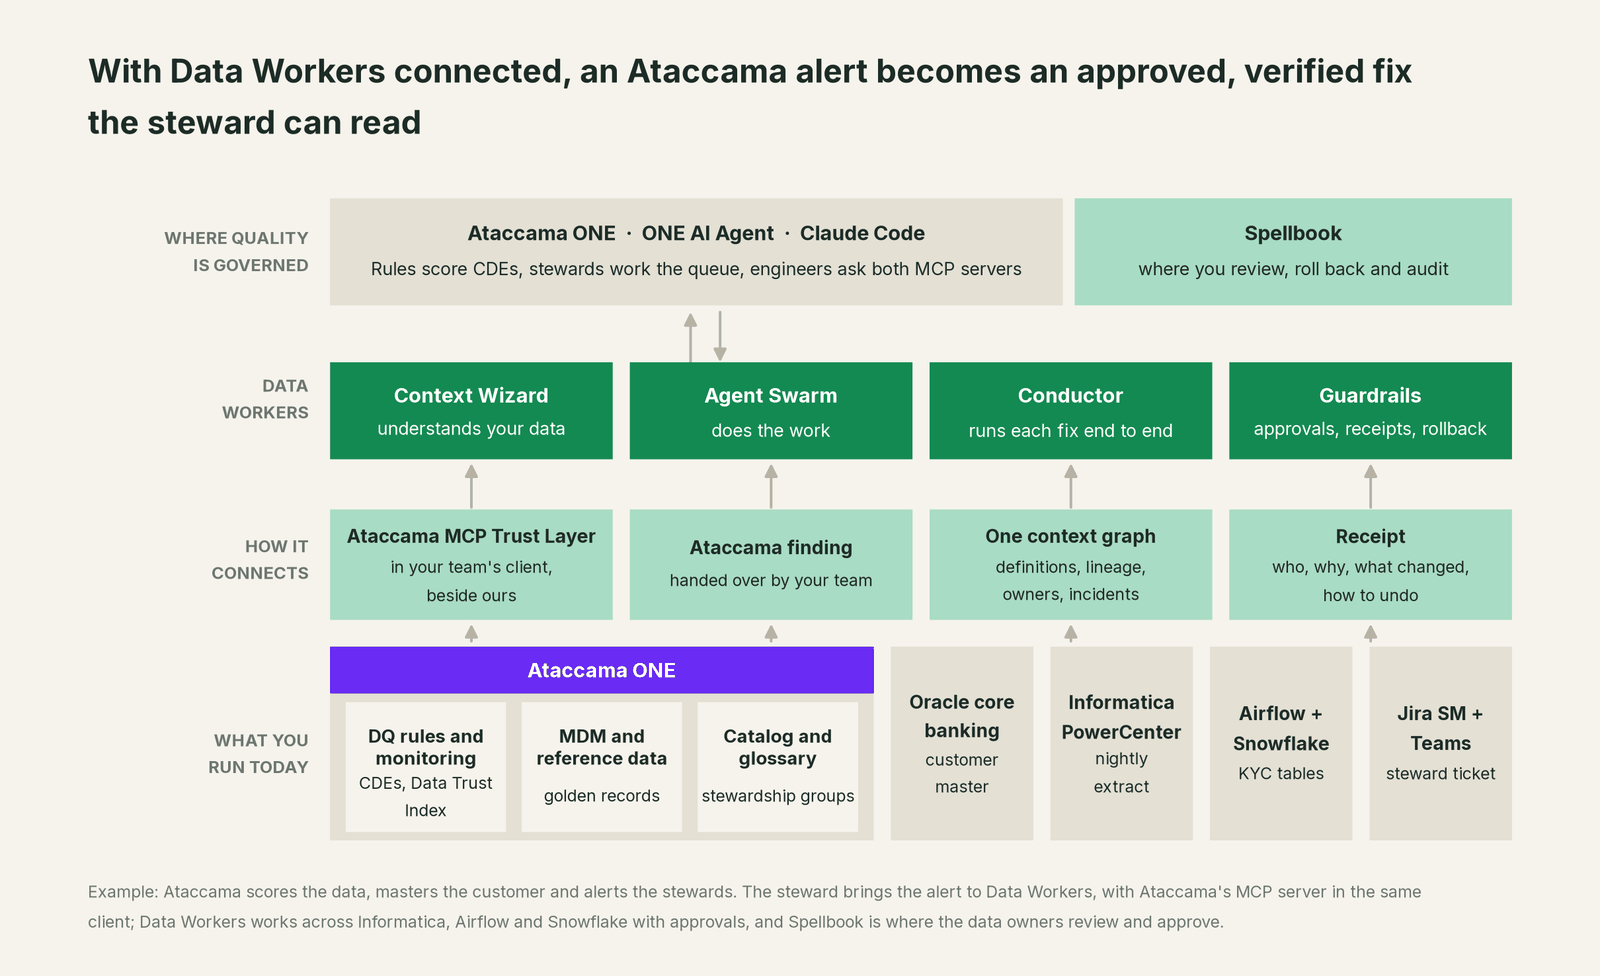
Ataccama to Data Workers. Data Workers connects to Ataccama over its API or MCP server today. The MCP Trust Layer gives it catalog items, terms, rules, DQ results, profiling and the Data Trust Index; the public APIs, generally available since October 2026, add alerts, their findings and the pipeline jobs Ataccama observes. Snowflake, Airflow, Jira Service Management and Teams are native Data Workers connectors. Oracle and Informatica PowerCenter connect over their APIs or MCP servers today, and the ETL team keeps running its own workflows.
An Ataccama alert starts a diagnosis. diagnose_incident and get_root_cause work the evidence, trace_cross_platform_lineage follows the data back through the pipeline, blast_radius_analysis maps every table, job and report downstream, run_quality_check confirms the truncated values in Snowflake, and get_incident_history checks for repeats. remediate proposes the change set. After approval, Data Workers queues the rerun through Airflow, run_quality_check and get_quality_score verify the result, and every step lands in get_audit_trail, a hash-chained log.
Data Workers to your stewards. Data Workers opens the Jira Service Management ticket, comments its diagnosis and receipt link, and posts finding and resolution cards to Teams; the steward resolves the ticket and the Ataccama alert.
Side by side in one client. Every Data Workers agent is an MCP server; the client setup guide documents the path: clone the open-source repo and add one start-agent.sh entry per agent. Example .mcp.json for Claude Code, with the Ataccama endpoint and M2M headers as Ataccama's documentation gives them:
{
  "mcpServers": {
    "ataccama": {
      "type": "http",
      "url": "https://<your-environment>.ataccama.one/private/api/mcppublic/mcp",
      "headers": {
        "X-Client-Id": "<client_id>",
        "X-Client-Secret": "<client_secret>"
      }
    },
    "dw-context-catalog": { "command": "/path/to/dataworkers-claw-community/start-agent.sh", "args": ["dw-context-catalog"] },
    "dw-incidents": { "command": "/path/to/dataworkers-claw-community/start-agent.sh", "args": ["dw-incidents"] },
    "dw-quality": { "command": "/path/to/dataworkers-claw-community/start-agent.sh", "args": ["dw-quality"] },
    "dw-schema": { "command": "/path/to/dataworkers-claw-community/start-agent.sh", "args": ["dw-schema"] }
  }
}
Ask "why did the Data Trust Index on customer.tax_id drop overnight, and what does the fix touch?" and the client calls both. Ataccama returns the CDE, the failing rule and the trust score; Data Workers returns the truncated port upstream, everything downstream and a proposed repair. For a shared endpoint, the Data Workers remote server takes an API key (bearer) or OAuth tokens from your identity provider, such as Okta or Entra ID, verified through JWKS.
One Ataccama alert, L0 to L4, set per domain:

- •L0 manual. The steward exports invalid records; the ETL team traces it by hand.
- •L1 observe. Data Workers posts the diagnosis and blast radius to the Jira ticket. Nothing changes.
- •L2 propose. The mapping change, reload and new check wait for the ETL owner's approval.
- •L3 act reversibly. For proven classes, such as a rerun after an approved fix, Data Workers queues it through Airflow and verifies it.
- •L4 autonomous. In a scoped domain with a clean record, repeatable steps run end to end; mapping changes still go to their owners.
For the safety model, read is it safe to let AI agents change production data and how approvals work. On where data lives: the agents run in your infrastructure and hold the credentials, your data stays in your systems, and the hosted Conductor sees workflow metadata only. For regulated estates, see Data Workers for financial services.
What changes for your team
Ataccama gave the governance office a score everyone trusts and a steward for every CDE. Data Workers gives those stewards a crew.
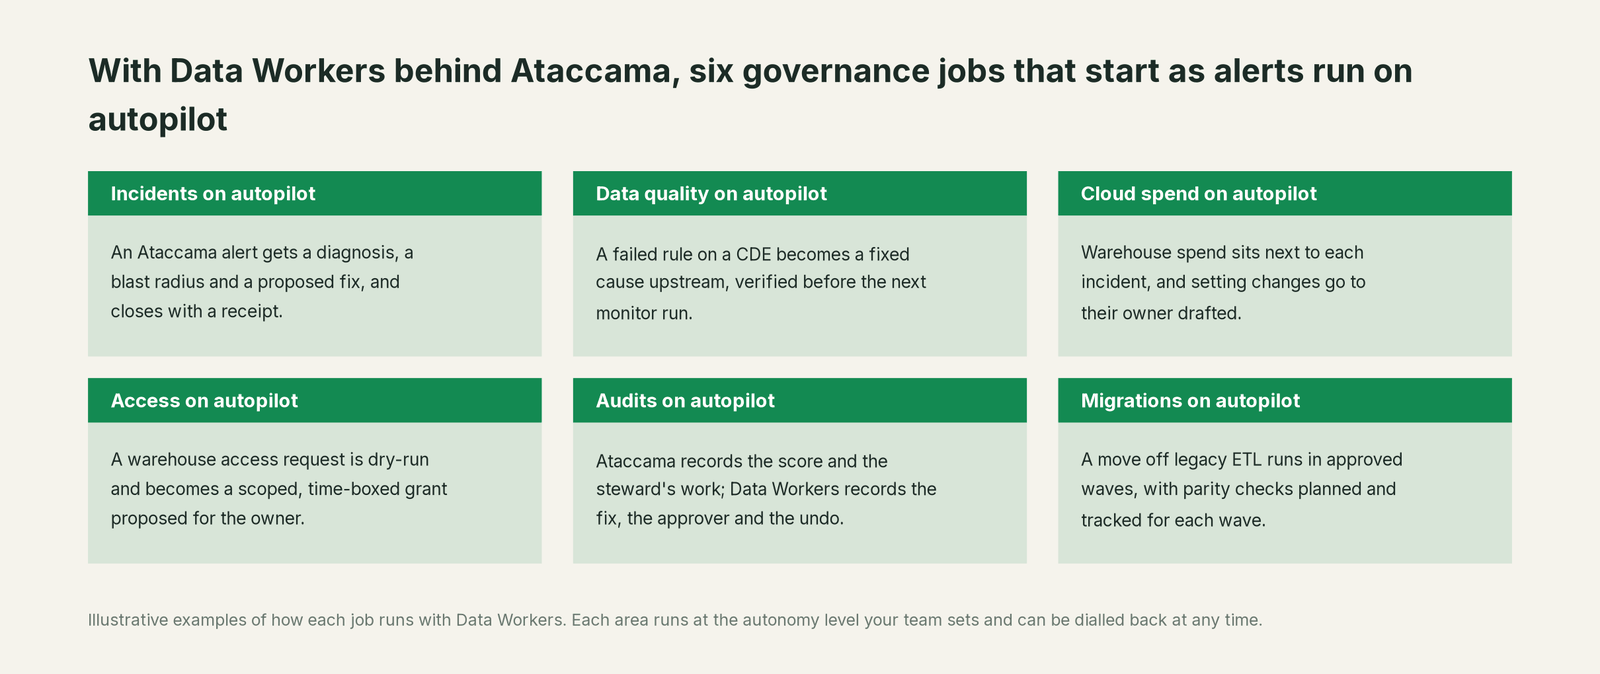
- •Incidents. An Ataccama alert arrives with a diagnosis, a blast radius and a proposed fix, and closes with a receipt.
- •Data quality. A failed rule on a CDE becomes a fixed cause upstream, verified before the next monitor run, with a new check where the break entered.
- •Cloud spend. Warehouse spend sits next to each incident, and setting changes go to their owner drafted.
- •Access. A warehouse access request is dry-run and becomes a scoped, time-boxed grant proposed for the data owner.
- •Audits. Ataccama records the score and the steward's work; Data Workers records what changed, who approved it and how to undo it.
- •Migrations. A move off legacy ETL runs in approved waves, with parity checks planned and tracked for each wave, and SQL translated into Snowflake. See tools that automate Teradata and Informatica migrations.
The stewards change most: their tickets already hold the cause and a fix awaiting one approval, so they spend their time on rules, definitions and golden records. Read Data Workers for data governance leads and who owns the agents.
Keep Ataccama, or consolidate?
Keep Ataccama if you love it; Data Workers works with it from day one. Many teams consolidate once Data Workers runs that slice too.
In regulated industries most teams keep Ataccama: MDM, reference data and a Data Trust Index the regulator has already seen are hard-won. What they consolidate is the work around it: hand-built remediation scripts, spreadsheets of open CDE issues and a second monitoring tool on the same tables. If you are weighing building the fix layer yourself on the MCP Trust Layer and a coding agent, read build it ourselves with Claude Code and MCP servers: the read calls are the easy part; the context graph, approvals, rollback and receipts are the work. Across the category, see you're on DQLabs, you're on Informatica Data Quality and you're on Collibra Data Quality.
The case for your CFO
The outcome: Ataccama tells the bank which data it can trust. Data Workers turns each broken CDE from days of cross-team tracing into a diagnosis on arrival and a complete fix behind one approval, so regulatory files and finance reports run on corrected data on schedule.
The risk story is plain. Autonomy is set per domain: L1 only reads; L2 changes nothing until a named person approves; L3 applies only changes it can undo. An unanswered approval request expires and escalates, never auto-grants. No agent can promote its own work. Every change carries a receipt: the cause, the change, who approved it, what it touched, how it was verified and how to undo it. An org-wide stop halts all autonomous dispatch. Zero migration: every system stays where it is.
Why now: Ataccama finds and scores the problem faster than ever, so the slow part is the fix across teams. The first win is read-only: every Ataccama alert in one domain gets a diagnosis and a blast radius, and rules, stewardship and change control stay the same. For the numbers, see the ROI of agentic data operations.
The sentence to repeat upstairs: "Ataccama tells us which data we can trust and who owns it; Data Workers fixes what breaks across our systems, with one approval, and proves it to the steward."
Getting started
Start with a pilot. Pick one governed domain such as KYC, connect Data Workers to Ataccama, Jira Service Management, your orchestrator and your warehouse, and run at L1 so every alert gets a diagnosis and a blast radius. Then turn on the first write class at L2, such as reruns after an approved fix. The pilot path and plans are on the pricing page, and the pilot is credited in full against the first year.
FAQ
How does Data Workers connect to Ataccama? Over Ataccama's API or MCP server today. The MCP Trust Layer exposes catalog items, terms, rules, DQ results, profiling and the Data Trust Index; the public APIs add alerts, findings and observed pipeline jobs.
The ONE AI Agent already creates rules and runs DQ evaluation. Why add Data Workers? The ONE AI Agent works on Ataccama's objects, with approval before each change. Data Workers works on the systems that produced the bad data: the cross-system diagnosis, the change set with its blast radius, a named approver, the queued reload, the verification and the receipt.
Does Data Workers change anything in Ataccama? No. Rules, monitors, MDM settings, reference data and stewardship stay with your Ataccama administrators, and Ataccama's MCP server is read-only by design. Data Workers reads, and its receipt lives in Spellbook, the audit trail and the linked ticket.
Does Data Workers close our Jira or ServiceNow tickets? No. It opens a ticket and comments its diagnosis and receipt link, or updates a ServiceNow ticket's summary and priority. The steward or service agent resolves the ticket, so your ITSM process and its records stay intact.
Can Data Workers fix the bad records or our Informatica mappings? It proposes. Mapping, pipeline and data-cleanup changes go to their owners to approve and apply. After approval, Data Workers queues the reruns through your orchestrator and verifies the result.
Our auditors need proof a CDE was fixed and stayed fixed. What do they get? A receipt per change: the cause, the change, who approved it, what it touched, the checks it passed and how to undo it, kept in a hash-chained audit trail.
Where does our data go? The agents run in your infrastructure and hold the credentials and model key, so your data stays in your systems. The hosted Conductor sees workflow metadata only.
Sources
- •Ataccama, homepage (site title "Ataccama: Agentic Data Trust Software"; modules, ONE AI Agent, MCP), https://www.ataccama.com/ (checked Oct 3, 2026)
- •Ataccama, MCP server page, https://www.ataccama.com/platform/mcp (checked Oct 3, 2026)
- •Ataccama Docs, Ataccama ONE Agentic overview, https://docs.ataccama.com/ataccama-one-agentic/latest/overview.html (checked Oct 3, 2026)
- •Ataccama Docs, AI Agent, https://docs.ataccama.com/ataccama-one-agentic/latest/gen-ai/ai-agent.html (checked Oct 3, 2026)
- •Ataccama Docs, AI Governance and Security, https://docs.ataccama.com/ataccama-one-agentic/latest/gen-ai/ai-governance-and-security.html (checked Oct 3, 2026)
- •Ataccama Docs, MCP Trust Layer for External AI Agents (read-only, endpoint, auth, tools), https://docs.ataccama.com/ataccama-one-agentic/latest/gen-ai/mcp-trust-layer.html (checked Oct 3, 2026)
- •Ataccama Docs, Connect to the MCP Trust Layer (Claude Code config, X-Client-Id and X-Client-Secret headers), https://docs.ataccama.com/ataccama-one-agentic/latest/gen-ai/install-mcp-trust-layer.html (checked Oct 3, 2026)
- •Ataccama Docs, Escalate Alerts (Jira and ServiceNow; escalation policies for ServiceNow), https://docs.ataccama.com/ataccama-one-agentic/latest/alerts/escalate-alerts.html (checked Oct 3, 2026)
- •Ataccama Docs, Send Notifications to MS Teams, https://docs.ataccama.com/ataccama-one-agentic/latest/alerts/ms-teams-notifications.html (checked Oct 3, 2026)
- •Ataccama Docs, Pushdown Processing (Snowflake, Databricks), https://docs.ataccama.com/ataccama-one-agentic/latest/data-processing/pushdown-processing.html (checked Oct 3, 2026)
- •Ataccama Docs, release notes October 2026 (public APIs generally available), https://docs.ataccama.com/ataccama-one-agentic/latest/release-notes/release-notes-october-2026.html (checked Oct 3, 2026)
- •Ataccama Docs, release notes September 2026 (read-only alerts API), https://docs.ataccama.com/ataccama-one-agentic/latest/release-notes/release-notes-september-2026.html (checked Oct 3, 2026)
- •Ataccama Docs, release notes August 2026 (rebuilt AI Agent, freshness SLAs, Data Quality API in Early Access Preview), https://docs.ataccama.com/ataccama-one-agentic/latest/release-notes/release-notes-august-2026.html (checked Oct 3, 2026)
- •Ataccama Docs, release notes July 2026 (cross-table rules), https://docs.ataccama.com/ataccama-one-agentic/latest/release-notes/release-notes-july-2026.html (checked Oct 3, 2026)
- •Data Workers open-source repository, https://github.com/DataWorkersProject/dataworkers-claw-community (checked Oct 3, 2026)
- •Data Workers client setup guide, https://dataworkers.io/opensource-docs/client-setup/ (checked Oct 3, 2026)